What Security Guard Companies Should Know About Cyber Security
Trackforce
October 5, 2016 · 14 min read
Small businesses are not collateral damage in cyber crime, they are the main target. Verizon’s 2026 Data Breach Investigations Report found that small and mid-sized organizations accounted for 96% of ransomware victims, and that attackers now break in most often through unpatched software rather than stolen passwords. With plenty of conflicting advice and preventative software available online, we wouldn’t blame a security guard company for not knowing where to start, or for that matter who to trust.
In this article, we’re going to discuss some best practices on how small security guard businesses can keep themselves safe from the very real threat of cyber attacks. First, let’s take a look at some of the main cyber security threats most small businesses face today:
Key takeaways
- Being small is not cover.
Small and mid-sized organizations make up the large majority of breach victims, because limited patching and recovery capability makes them the easier target. - A guard company holds unusually sensitive data.
Client site plans, access procedures, incident reports and officer records are all valuable to an attacker, and all of it sits in systems somebody has to secure. - Your vendors are now part of your attack surface.
Breaches involving a third party have risen sharply as a share of the total, so the security of the software you run is genuinely your problem too. - The basics still do most of the work.
Multi-factor authentication, prompt patching, least-privilege access and trained staff prevent far more incidents than any single product purchase. - TrackTik is built to be the secure place that data lives.
Trackforce holds SOC 2 Type II, ISO 27001 and ISO 27017 certification, encrypts data at rest and in transit, and commissions external penetration tests several times a year.
What are the biggest cyber threats to small businesses?
1. Phishing and social engineering
Phishing means sending fraudulent messages in the hope of fooling the victim into handing over their credentials, which leaves them open to attack. It remains one of the most effective routes in, and Verizon’s 2026 report attributes roughly 62% of breaches to the human element.
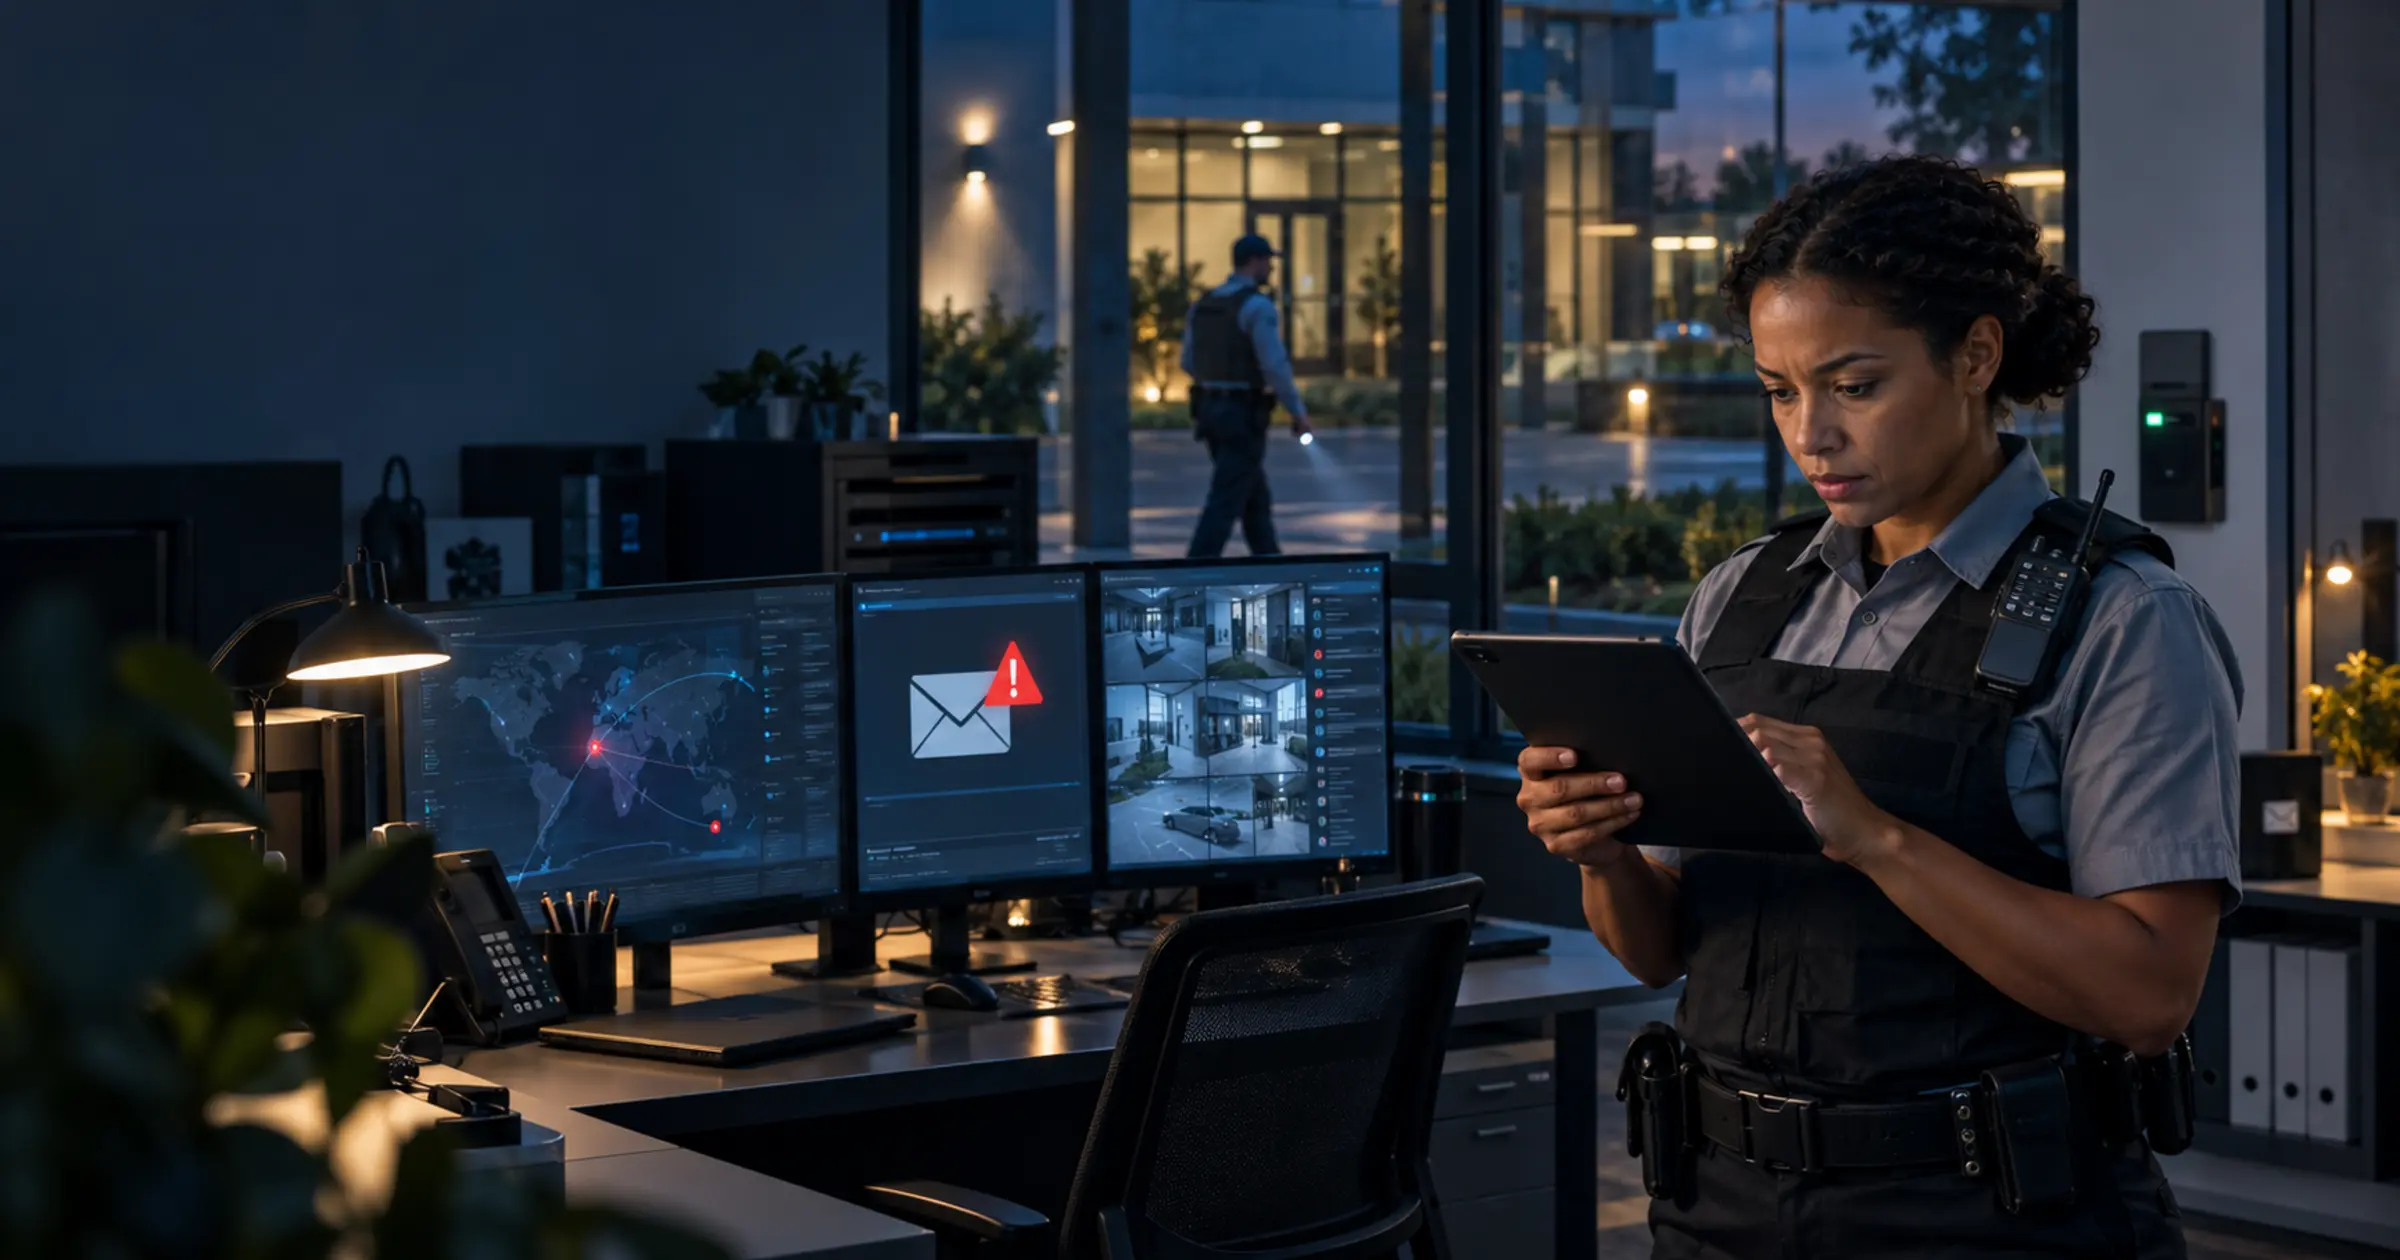
What has changed is the channel. Phishing by text message and phone call now succeeds noticeably more often than email phishing in tested scenarios, which matters a great deal in this industry because your officers work from phones all shift. A convincing text claiming to come from dispatch is a very different problem from a suspicious email on an office desktop.
These attacks are often aimed at whoever handles payroll or supplier payments, and they can put a company’s entire financial position at risk, with criminals potentially gaining access to funds and other vital information.
2. Client and customer account compromise
Another very real threat is criminals targeting a company’s data in order to reach client accounts, or compromising a client device to get there. Once inside, it becomes possible to make fraudulent transactions and steal client data.
For a guard company the exposure is wider than payment details. A client relationship often includes site access procedures, alarm response instructions, patrol schedules and contact trees. That is a package an attacker can use for physical entry as well as fraud, which is exactly why cyber security matters to the physical security industry rather than being somebody else’s department.
3. Data and intellectual property leaking out
Intellectual property theft is a long-standing problem for businesses developing new systems, pricing models and processes to get ahead of competitors. Attackers gaining access to a company’s systems in order to copy that work is real, and more common than owners assume.
The newer version of this risk is self-inflicted. Verizon’s 2026 report found employee use of AI tools roughly tripled, to around 45%, and that most of those users reached AI services through personal rather than corporate accounts on work devices. Every post order, client report or bid document pasted into a personal AI account is company and client information leaving your control without anybody attacking you at all.
What A Guard Company Holds That Attackers Want
Generic cyber advice tends to assume your most sensitive asset is a card number. In contract security it usually is not. Working out what you actually hold, and where it lives, is the step that makes everything after it easier to prioritise.
| What you hold | Why an attacker wants it |
|---|---|
| Site access procedures and alarm codes | Turns a digital breach into physical entry at a client site |
| Patrol schedules and post orders | Shows exactly when a location is unattended |
| Incident reports and photographs | Client-confidential detail, often legally sensitive |
| Officer records and payroll data | Identity theft and payment redirection fraud |
| Contract rates and bid documents | Commercially valuable to a competitor |
Notice that almost every row is client information rather than your own. That is the part worth sitting with, because a breach at your company becomes a breach conversation with every account you serve. Keeping that material inside one controlled system, rather than spread across spreadsheets, personal email and messaging apps, is the single biggest reduction in exposure most firms can make. In TrackTik it lives in guard management, incident reporting and the back office suite under one access model.
How small security guard businesses can protect themselves
So, how can small security guard businesses prepare themselves for the rising threat of cyber attacks? The simple answer is to take preventative measures now, rather than be sorry later.
Below, we’re going to discuss some advice and best practices for better cyber security.
1. Talk Strategy with an IT Expert
We’re aware that not all small businesses will have their own IT departments, so if not, it’s time to bring an expert in for a bit of advice about how to best prevent cyber attacks in future.
2. Keep Staff Trained and up-to-speed
Staff training plays a crucial role in keeping businesses safe from cyber security threats. Guards should be informed about using strong passwords, what to do if they receive a suspicious email or text, and general security awareness. Given how much of the attack volume now arrives by phone and message, make sure that training covers the handset and not just the desktop.
3. Update Software Regularly
It’s important to ensure all your software is kept up-to-date, including anti-virus protection and security software. We’d also recommend using anti-spyware and malware removal tools for additional protection against attacks.
This has become the highest-value item on the list rather than routine housekeeping. Unpatched software is now the most common way attackers get in, and the gap between a flaw becoming public and being exploited has shortened dramatically. Automatic updates on phones, laptops and network equipment are worth more than most paid security products.
In the event that anti-virus software is unable to remove something suspicious installed on an employee’s computer, they should immediately contact an IT specialist for assistance.
4. Turn On Multi-Factor Authentication Everywhere
If you do one technical thing this quarter, make it this. Multi-factor authentication on email, payroll, your guard management platform and any remote access tool removes most of the value of a stolen password. Prioritise anything reachable from the public internet, and anything that can move money.
5. Give People Only The Access They Need
A supervisor covering three sites does not need visibility of every client in the business, and a former employee should lose access the day they leave. Role-based permissions and a genuine offboarding checklist limit how far any single compromised account can travel, which is easier to enforce when joiners and leavers are handled in one place through people management rather than remembered account by account. This is also where an audit trail earns its place, because reporting on who accessed what is how you answer a client asking whether their data was touched.
Your Software Vendor Is Part Of Your Attack Surface
This is the change that most small security firms have not caught up with. Breaches involving a third party have climbed steeply and now account for something close to half of all breaches, according to Verizon’s 2026 report. In practice that means the weakest system holding your client data may not be one you administer at all.
For a guard company that is a short list: your guard management platform, your payroll provider, your email host, and any subcontractor with a login to your systems. Each one deserves the same question you would ask about a new officer, which is what are they trusted with and how do we know they can be.
Five questions worth putting to any vendor before you sign, and to your current ones at renewal:
- Are you independently audited, and can I see the report? SOC 2 Type II and ISO 27001 mean an external auditor has tested the controls rather than the vendor describing them. Ask for the current report, not the badge on the website.
- How is my data encrypted, at rest and in transit? Both, not one. Encryption in transit alone still leaves a readable copy in the database.
- Do you support single sign-on and role-based permissions? Without these you cannot enforce your own access policy inside their product, which quietly undoes the work from the previous section.
- How often are you penetration tested, and by whom? Annual internal testing is a much weaker answer than regular external testing by a specialist.
- What happens to my data when I leave, and where is it held? Get the data processing agreement, the hosting region and the deletion terms in writing, particularly if you operate across borders.
For the record, here is how Trackforce answers those questions for TrackTik. The platform is certified against SOC 2 Type II with a yearly audit, ISO 27001 for information security management and ISO 27017 for cloud security, and is aligned to NIST SP 800-171 alongside GDPR and CCPA requirements. Data is hosted on AWS in your region, encrypted at rest and in transit, with daily backups and key management through AWS. Access follows least-privilege principles with single sign-on support, external penetration tests run several times a year, and centralised logging provides the traceability an audit needs. The full detail, including how to request the data processing agreement or a current audit report, is on the Trackforce trust page.
Ask a prospective vendor for their most recent independent audit report. A company that treats security seriously will have one ready, and the ones that hesitate have told you something useful.
A Practical Cyber Checklist For A Guard Company
None of this needs a security department. Working through the following in order will move a small firm further than buying another tool.
- Write down where client data actually lives. Include the spreadsheets, the shared mailbox and the messaging group, because those are usually the least protected places on the list.
- Switch on multi-factor authentication for email, payroll and your operations platform this week.
- Turn on automatic updates across phones, laptops, routers and cameras, then check that they are genuinely applying. You cannot patch equipment you have not inventoried, so keep a current list of company devices, ideally in asset tracking rather than somebody’s memory.
- Review who has access to what and remove every account belonging to someone who has left.
- Agree an AI rule with your team. Decide which tools are approved and make clear that client reports and post orders do not go into personal accounts.
- Brief officers on text and phone scams using a real example, and give them one named person to verify anything unusual with.
- Ask your vendors the five questions above and keep the answers on file for client due diligence.
- Test that you can restore from backup. An untested backup is a plan, not a capability.
Clients are increasingly asking about this during procurement, so being able to answer confidently has become part of winning work rather than just protecting it. If you serve larger accounts, our enterprise security pages cover the standard of documentation those buyers expect, and converging physical and cyber security looks at where the two disciplines are heading.
TrackTik from Trackforce is built so the operational data your business runs on sits in an independently certified platform rather than on paper and spreadsheets. If you want to see how it handles access control, audit trails and client reporting, you can request a TrackTik demo, or read more about the TrackTik platform first.
Frequently Asked Questions
Latest Articles
Featured Resources
See Trackforce in action
Book a walkthrough with our team and see how it fits your operation.