What’s In a Report? Physical Security Incident Reporting the Right Way

Trackforce
December 11, 2024 · 11 min read
Creating a clear and effective security guard incident report can be challenging. While it’s a fundamental aspect of physical security, poor reporting can harm your company’s reputation.
The good news is that you can improve your reports significantly. Many companies still rely on paper or basic online reports, which might not provide the information you need. Digital reporting, on the other hand, offers access to data and analytics that traditional methods cannot match.
In this blog, we dive into why digital incident reporting is essential for your officers, and what separates a report that holds up from one that does not.
Key takeaways
- A report has more than one audience.
The client, a supervisor, an insurer, a lawyer and your own reporting all need different things from the same record, and a format that serves only the client fails the rest. - Captured beats entered.
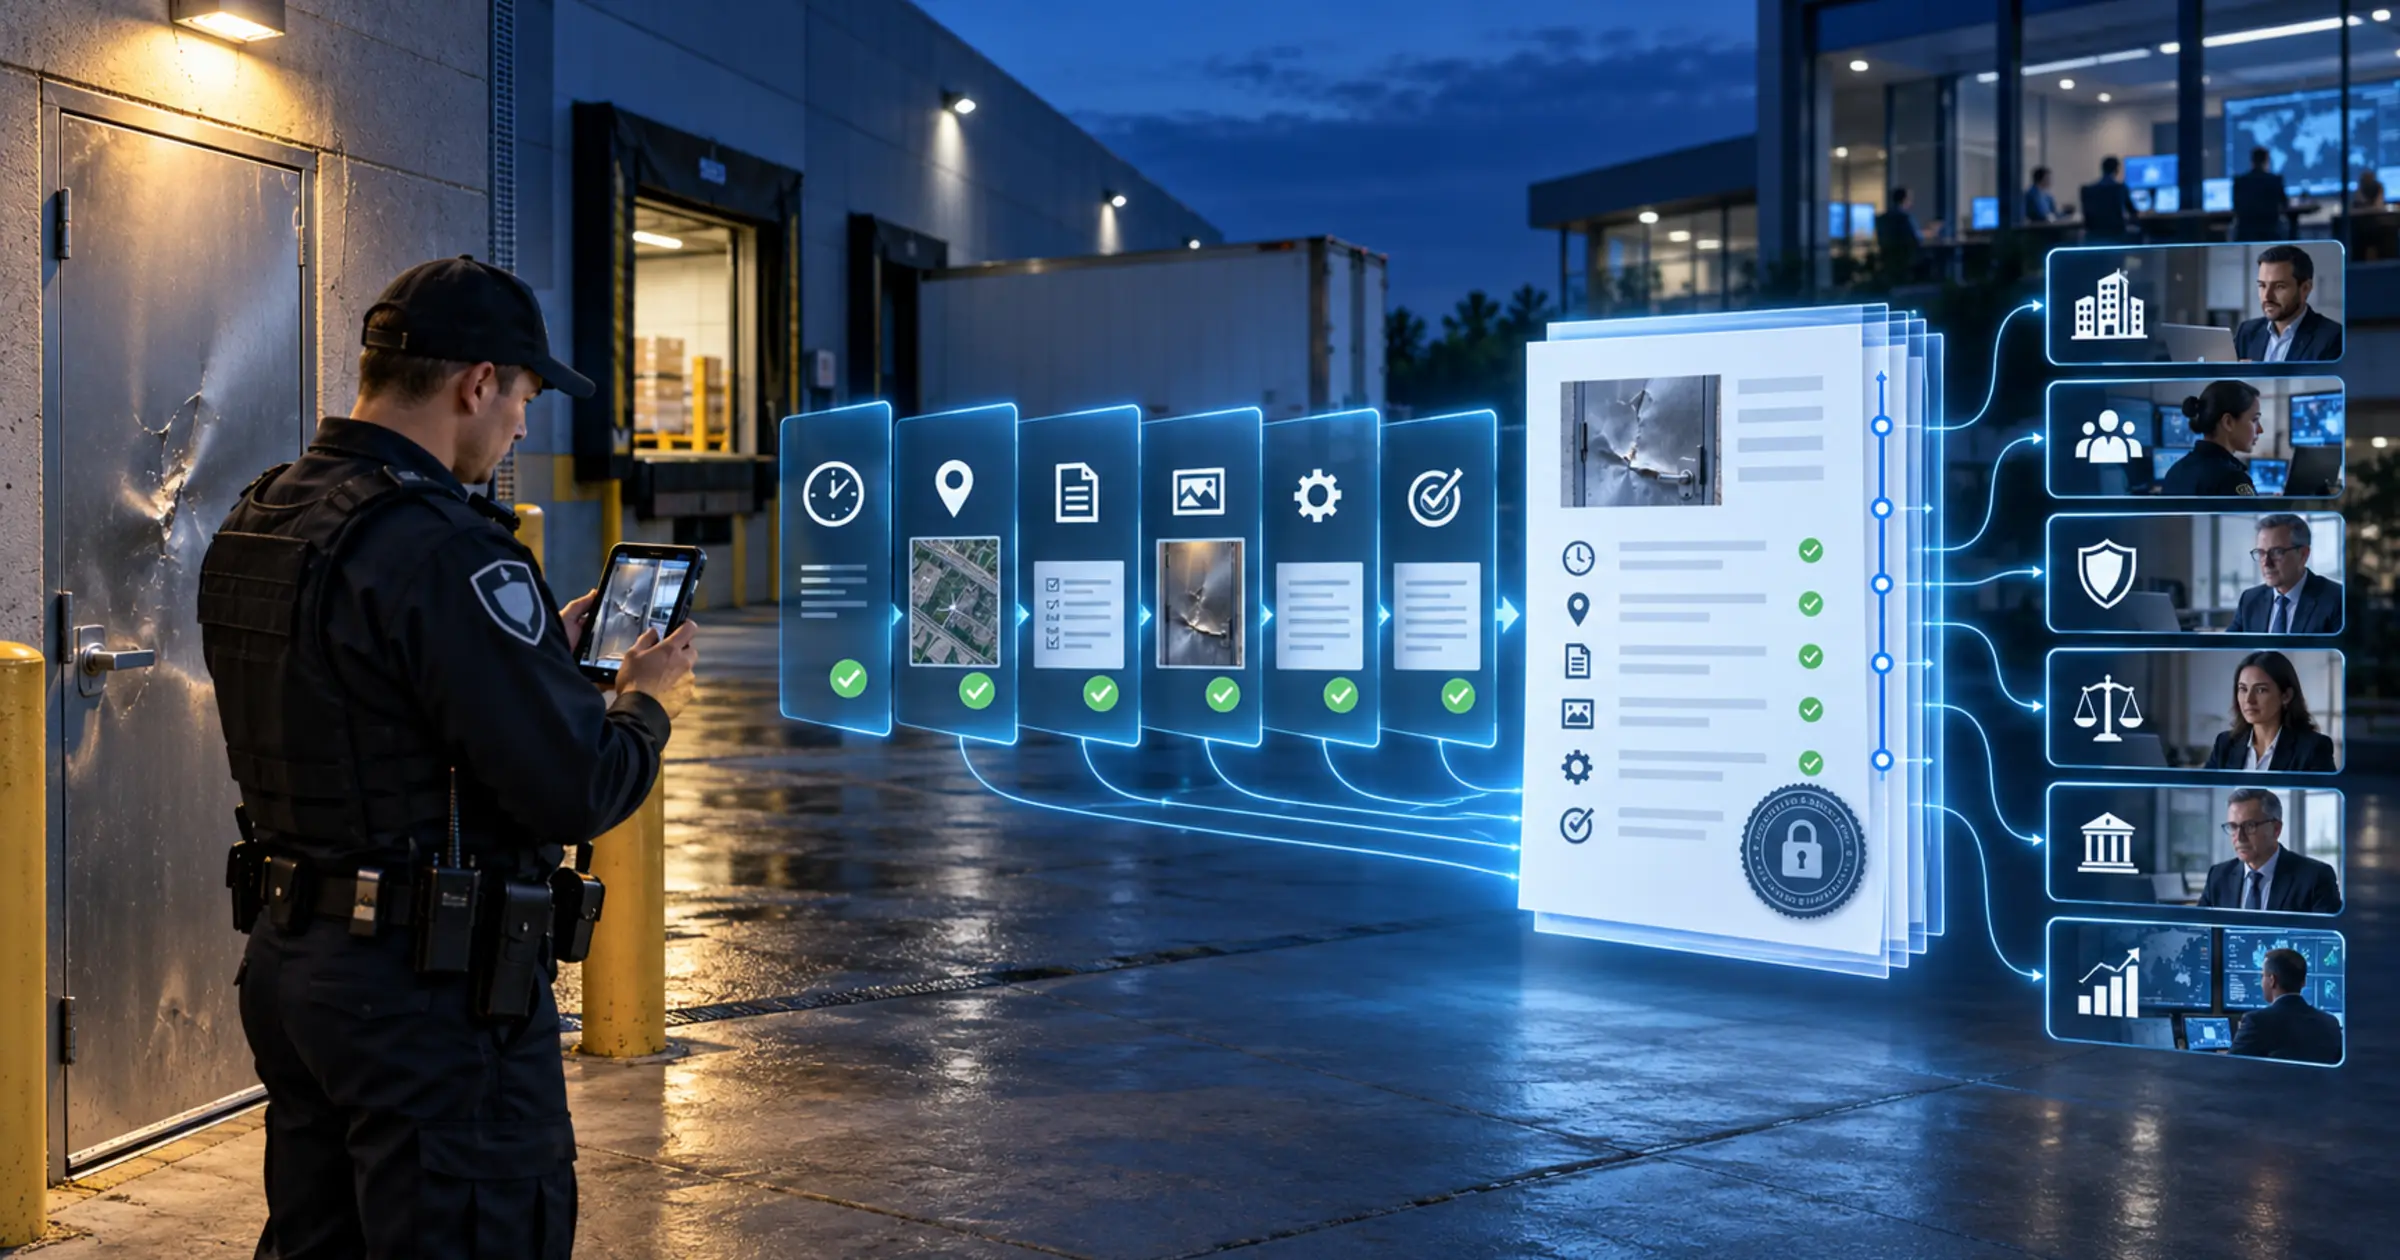
A time an officer typed is a recollection. A timestamp, a GPS position and a scanned checkpoint are records, and only one of those survives a dispute. - Free text cannot be counted.
Without a required category, an incident can be read but never trended, which is how firms end up with thousands of reports and no insight. - Reporting bias is a training problem, not a form problem.
Officers under-report when they are unsure whether reporting is welcome. No template fixes that. - An audit trail is what makes a report defensible.
If reports can be edited with no trace of what changed, the entire record becomes arguable months later.
Security guard incident reports
Good reporting means understanding and documenting the facts. However, capturing these facts can be tough if your security guards aren’t trained to write effectively. There is a fuller walkthrough in our guide to improving officer report writing.
Here are some tips for tightening up your incident reporting process
- Overcoming reporting bias: Reporting bias is a real issue. To counter it, officers must feel comfortable and supported in reporting what they observe without hesitation.
- Aligning with SOPs and contracts: Check your Standard Operating Procedures (SOPs) and contract guidelines to determine what your reports need to include. Detailed reports help justify your officers’ actions and meet contract requirements, and they are what make the hours you bill through contracts and invoicing defensible.
- Organizing reports: For reports with special requirements, ensure they are organized so officers know which ones need extra attention.
Let’s dive into other best practices for your incident reports.
Standardize your reports
Improving reporting standards involves understanding the basics, creating an easy-to-follow template, and making sure the process is repeatable.
Know your reporting basics
Find repeatable elements
Even though reports repeat, they should be adaptable for use in various situations. A standardized template helps officers quickly identify and report essential information to support your SOPs. Our piece on configurable reporting templates goes into how that works in practice.
Create a report template
Not all templates are the same. A comprehensive template should be flexible enough to accommodate additional details when necessary, such as regulatory requirements. When shifting from paper to digital reporting, consider looking for:
In practice most of that list is a mobile app question rather than a desktop one, because the officer needs to file in-tour rather than writing it up at the end of a shift from memory.
Train your guards
Effective training for security officers is crucial since they are the first responders to incidents and are the ones filling out the reports. They need to be calm and confident when completing reports.
Improving soft skills
Soft skills are important for security officers. By enhancing their listening and writing skills, you can improve the quality of their reports. Focus on training in:
Consider these aspects as well when training your teams
One thing worth separating out: writing quality and willingness to report are different problems. Training fixes the first. Only culture fixes the second, because an officer who suspects that reporting an incident will create trouble for them will keep writing short reports no matter how good the template is. Where writing is genuinely the barrier, ReportPro AI helps by turning rough field notes into a readable report while keeping the officer’s original text and a field-level audit log alongside it, which matters for the reasons below.
Who actually reads the report
Most reporting advice treats the client as the only audience. In reality a single incident report may be read by five different people with five different requirements, and a format that serves one can quietly fail the others:
|
Who reads the report |
What they need from it |
What makes it fail for them |
|---|---|---|
|
The client |
Confirmation the site was covered, what happened, and what you did about it |
Narrative with no outcome, or a report that arrives a week later |
|
Your supervisor |
Enough detail to decide whether to escalate, within minutes |
Free text with no category, so it cannot be triaged or counted |
|
An insurer handling a claim |
Time, location and condition evidence captured at the moment |
A time the officer typed in afterwards rather than a timestamp |
|
A lawyer, months later |
An unaltered record with a traceable chain of custody |
Reports edited after the fact with no audit trail of what changed |
|
A regulator or auditor |
Consistency across officers and sites, and retention you can prove |
Every officer writing to their own format |
|
Your own reporting |
Structured fields that can be aggregated into a trend |
Detail buried in prose, which counts for nothing at the portfolio level |
The last row is the one firms notice last. Detail written into prose is invisible at portfolio level, which is why business intelligence depends on structured fields rather than better writing.
Signs your reports are not defensible
Worth checking before you find out the hard way. Any of these will undermine a report that is otherwise well written:
Standardize reporting in 30 days
- Days 1 to 7: collect every format in use. Gather the report types actually circulating across your sites. Most firms find more variants than they expected, several undocumented and a few invented locally by a supervisor.
- Days 1 to 7: check them against the contract. Read what each client contract and your SOPs actually require. This is where you discover you are either under-delivering or producing reports nobody asked for.
- Days 8 to 14: fix the required fields. Time, location, category, action taken, outcome. Make them mandatory rather than optional, and resist adding anything a reader will not use.
- Days 15 to 21: pilot on one site, filed in-tour. Have an officer complete it mid-shift on a phone, not a manager at a desk. Their first attempt tells you which fields are ambiguous.
- Days 22 to 30: show a client and set the review cadence. Their reaction is the real test of whether the template captures anything they value. Agree now what gets reported monthly so it survives the first busy period.
Reporting, the right way
Your company’s reputation is at risk if officers don’t know how to report incidents properly. Poor reporting can lead to lost client confidence and legal liabilities.
Ensure your officers can write reports clearly and understand your SOPs. Additionally, invest in robust reporting software that meets your basic or comprehensive needs. Tying it to guard management and tour verification is what turns individual reports into a record of the whole service.
Transitioning your incident reporting process to digital will result in better efficiency and deeper insights across your operations. If you are still working in paper, start with the case for going paperless with your daily activity reports and what every daily activity report should include. When you are ready, book a TrackTik demo and we will walk through it against one of your own sites.
Frequently Asked Questions
Latest Articles





Featured Resources





See Trackforce in action
Book a walkthrough with our team and see how it fits your operation.